6. Compliance Infrastructure: Audit Trails, Policy-as-Code, and the Append-Only Principle
TL;DR We had an AuditLogger that wrote to Loki only — the audit_events Postgres table sat empty for weeks. We had OPA running on a static policy…

5. Red-Teaming AI: OWASP LLM Top 10 and the Probes You Actually Need
TL;DR We had heard of the OWASP LLM Top 10, and we had implemented fewer than half of it. We had PyRIT installed, and we had almost…
4. Securing Agentic AI: Authentication, Authorization, and PII
TL;DR Our five-agent banking AI platform had OPA wired into exactly one agent. The MCP server had no auth middleware. All five agents shared one API key….
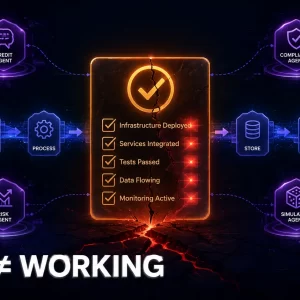
3. The 57-Gap Audit — What “Done” Actually Means in Production AI
TL;DR After weeks of building a multi-agent AI platform — five agents, full pipeline, red-team harness, control UI — the system looked done. It wasn’t. A config…
2. The Engineering Platform: Orchestration, Monorepo, and the Stack Decisions
TL;DR Once you decide to build a multi-agent AI system, you face three engineering choices that will determine whether the platform is governable or just functional: what…
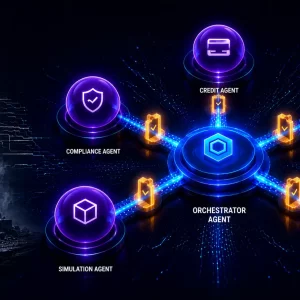
1. From Monolith to Multi-Agent — Why One AI Is Not Enough for Regulated Finance
TL;DR A single AI agent cannot safely handle a regulated financial decision. The problem is not capability — it is separation of concerns, auditability, and governance accountability….